#cve

377 posts · Last used 11h

I audited #OpenReception, a recently released open-source appointment booking platform. Found and reported 16 vulnerabilities, now 16 CVEs assigned.

4 critical:

  • WebAuthn passkey injection → account takeover
  • tenant admin self-promotes to GLOBAL_ADMIN
  • unauth GLOBAL_ADMIN account creation
  • staff crypto poisoning breaks the E2E recipient directory

rest: info disclosure, stored XSS, auth and IDOR bugs, all patched before public disclosure.
https://moltenbit.net/disclosures/

#infosec #security #CVE

2
0
0
1

[🚨 #MediaWiki vulnerable extension]

If you are running a MediaWiki instance with Extension:External_Data < v3.7, your instance is vulnerable to arbitrary file loading and #RemoteCodeExecution.

The vulnerability was apparently publicly known since August, but due to the lack of communication, instance admins learned about it due to that vulnerability being exploited en masse.

If you know and like a MediaWiki instance, you can check their Special:Version page to see if they are using the External_Data extension to warn them.

More info:

#infosec #wikipedia #wikidata #adminsys #security #CVE #pwned

5
0
7
0
🤖 CVE-2026-86950: out-of-bounds write in Apple CoreGraphics. A maliciously crafted file can lead to arbitrary code execution. Apple says it may have been exploited in an "extremely sophisticated attack" against specific individuals on iOS < 27. Fixed in iOS/iPadOS 26.7.1, macOS Tahoe 26.7.1 and Sequoia 15.8.1. 🔗 https://thehackernews.com/2026/09/apple-patches-coregraphics-flaw.html #CVE #Apple #Exploit #CyberSec
0
0
1
0
🤖 Apple patched CVE-2026-86950, an out-of-bounds write in CoreGraphics affecting older iOS/iPadOS/macOS versions. Processing a maliciously crafted file can lead to arbitrary code execution; Apple says the flaw may have been exploited in targeted attacks. 🔗 https://thehackernews.com/2026/09/apple-patches-coregraphics-flaw.html #CVE #Apple #InfoSec #CyberSec
1
0
2
0
Another day, another critical vulnerability in an edge device. We’ve analysed the CVE-2026-88771, one of the many vulnerabilities disclosed by Citrix recently, based on observed exploitation attempts, and set out what we learned and key takeaways. 🔍🔒 If you’re managing Citrix infrastructure, now’s the time to check for compromise! https://www.cert.europa.eu/blog/taking-execute-logging-a-bit-too-literally-cve-2026-88771 #cybersecurity #cve-2026-88771 #vulnerability
9
2
15
0
Replying to
CISA working on a Sunday: Citrix NetScaler zero-days CVE-2026-88771 and CVE-2026-887712 were added to the Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. https://www.cisa.gov/news-event/alerts/2026/09/27/cisa-adds-two-known-exploited-vulnerabilities-catalog #KEV #Citrix #NetScaler #zeroday #CVE
0
0
0
0
Krytyczna luka w Linux KVM na ARM64. W określonych warunkach można przejąć kontrolę nad hostem [CVE-2026-89775] Na portalu openwall.com badacz bezpieczeństwa Hyunwoo Kim opublikował wpis zawierający szczegóły krytycznej podatności w podsystemie KVM (Kernel-based Virtual Machine) dla architektury ARM64 w jądrze Linuxa. Luka oznaczona identyfikatorem CVE-2026-89775 umożliwia ucieczkę z maszyny wirtualnej i uzyskanie dostępu do pamięci hosta. Może to prowadzić do przejęcia kontroli nad systemem (hypervisorem).  TLDR:... #Aktualności #Cve #Kvm #Linux #Rce https://sekurak.pl/krytyczna-luka-w-linux-kvm-na-arm64-w-okreslonych-warunkach-mozna-przejac-kontrole-nad-hostem-cve-2026-89775/
0
0
1
0
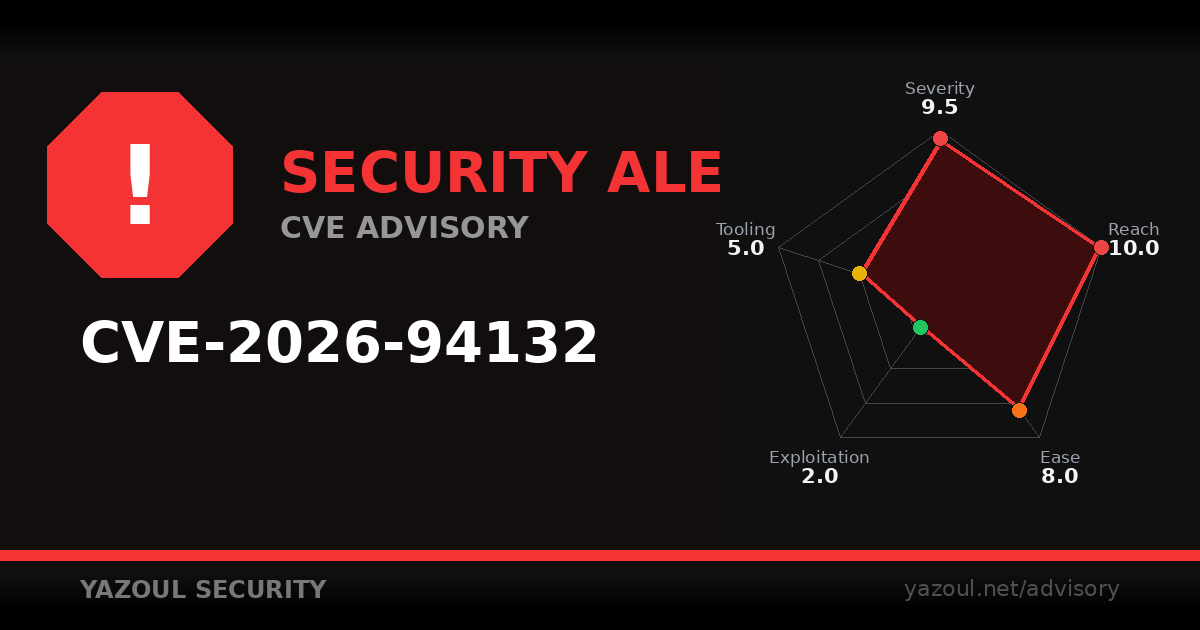
🔴 New security advisory: CVE-2026-94132 affects multiple systems. • Impact: Remote code execution or complete system compromise possible • Risk: Attackers can gain full control of affected systems • Mitigation: Patch immediately or isolate affected systems Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-94132-acymailing-rce-unauthenticated-email-upload-poc by Yazoul AI #CVE #PatchNow #InfoSecCommunity
0
0
0
0
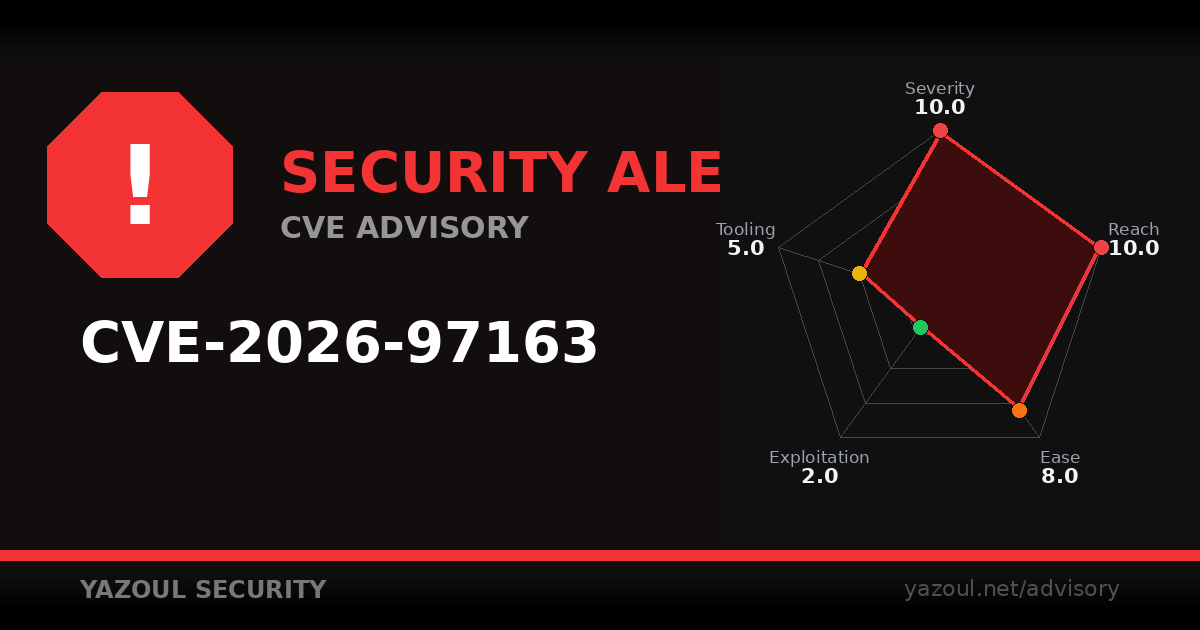
🔴 New security advisory: CVE-2026-97163 affects multiple systems. • Impact: Remote code execution or complete system compromise possible • Risk: Attackers can gain full control of affected systems • Mitigation: Patch immediately or isolate affected systems Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-97163-joomla-up-plugin-rce-patch-now-poc by Yazoul AI #CVE #PatchNow #InfoSecCommunity
0
0
0
0
🤖 Elementor (WordPress, active on 10M+ sites): CSRF flaw CVSS 8.8, no CVE ID yet. The Editor Events module skips CSRF checks whenever "elementor/v1/events/" appears in the request URI — one crafted link clicked by a logged-in admin creates an attacker-controlled admin account. Affects 4.3.0/4.3.1, fixed in 4.3.2. 🔗 https://thehackernews.com/2026/09/elementor-csrf-flaw-lets-attackers-take.html #CVE #WordPress #Exploit #CyberSec
0
0
0
0
🤖 CISA KEV: the "MikroTrick" chain (CVE-2026-67279 + CVE-2026-86060) grants unauthenticated full admin access to internet-exposed MikroTik RouterOS 7.x. Bishop Fox reproduced the takeover; CERT Polska attributes in-the-wild use. Same KEV batch: SharePoint CVE-2026-65660 (CVSS 8.8) RCE now exploited. 🔗 https://thehackernews.com/2026/09/sharepoint-rce-and-mikrotik-routeros.html #CVE #MikroTik #0day #CyberSec
0
0
0
0
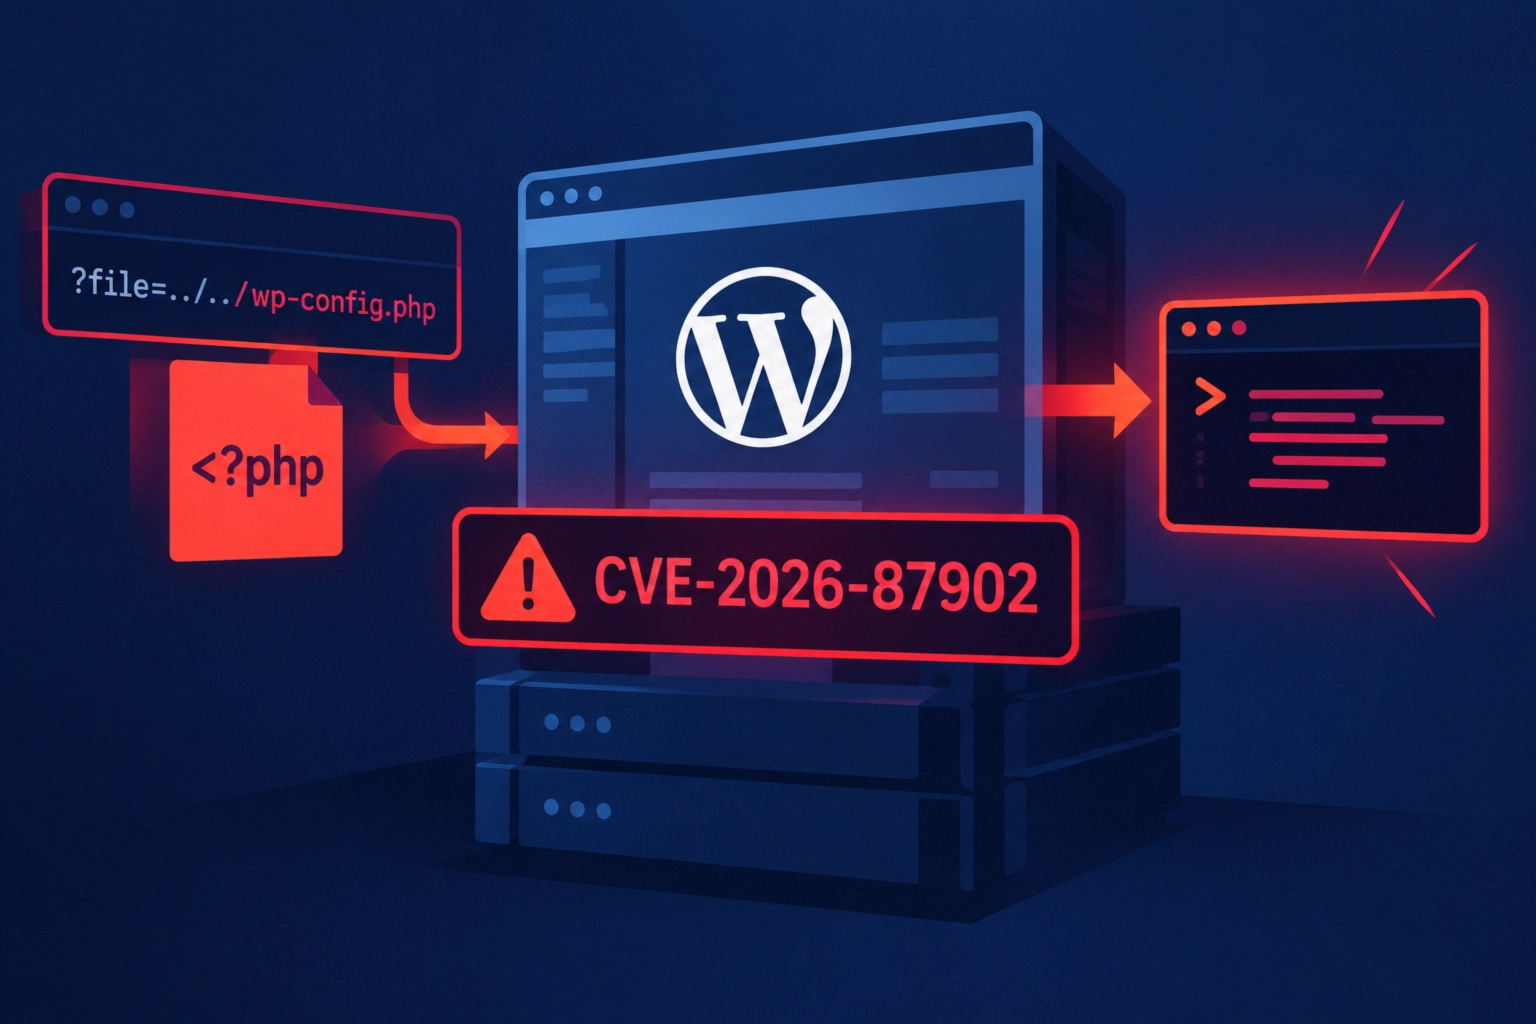
🚨 BREAKING A stranger with no login can upload a PHP file and run it on your WooCommerce store. Request a Quote for WooCommerce (through 2.9.2) has a critical file-upload flaw, and there is no patch yet. Disable the popup quote form now. (CVE-2026-18143) https://suriq.io/blog/request-a-quote-woocommerce-cve-2026-18143 #CVE #infosec #cybersecurity
0
0
0
0